Cybersecurity

Explanatory articles about digital risks, information protection, privacy, system resilience, and common misconceptions about security. This section focuses on understanding threats and principles of protection without providing instructions for abusing vulnerabilities.

A laptop screen showing cybersecurity compliance documents and a software inventory for the EU Cyber Resilience Act
Cybersecurity

When Software Grows a Legal Spine: Inside the EU’s Cyber Resilience Act

For years, building secure software in Europe meant following your own conscience — or your customer’s contract. You could ship a container image with no software inventory, patch vulnerabilities on whatever schedule suited you, and disclose flaws only if you felt like it. Good teams did better than that anyway, because it was good engineering. But nothing in EU law forced anyone to. The Cyber Resilience Act (CRA) changes that calculus: it takes practices security-conscious teams already knew were “best practice” and turns them into conditions for selling a product in Europe at all.
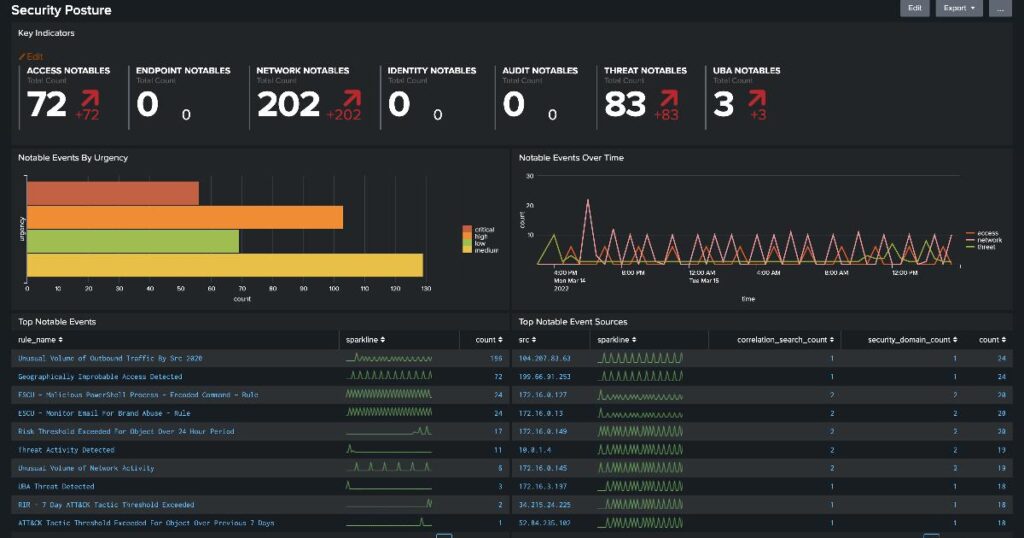
Security analyst reviewing event security threat intelligence for fake domains and online chatter linked to a major venue
Cybersecurity

When a Fake Ticket Site Is the First Sign of a Real-World Threat

Weeks before a stadium fills or a parade route closes to traffic, a different kind of activity is often already underway: someone registers a domain that looks almost like the official event site, a scam vendor lists a “sold out” hotel room that doesn’t exist, and a name that matches a VIP’s travel schedule surfaces in a chat channel nobody official is watching. None of that looks like a security emergency. But taken together, these small digital traces are frequently the earliest form of warning that a major event’s security team will ever get — long before anyone reaches a checkpoint.

Scroll to Top